In the product
Integrations and webhooks
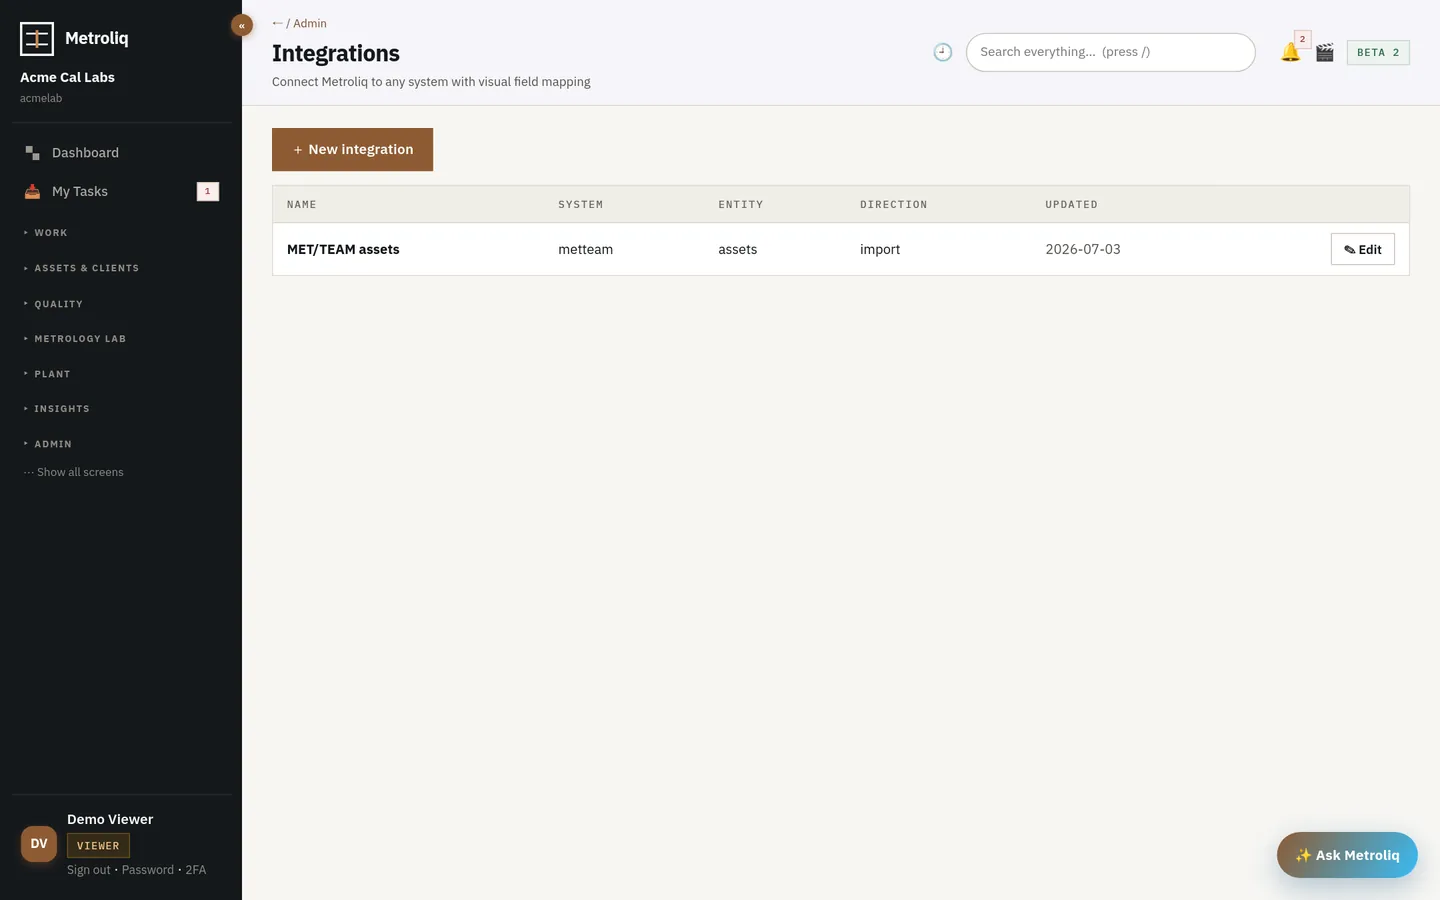
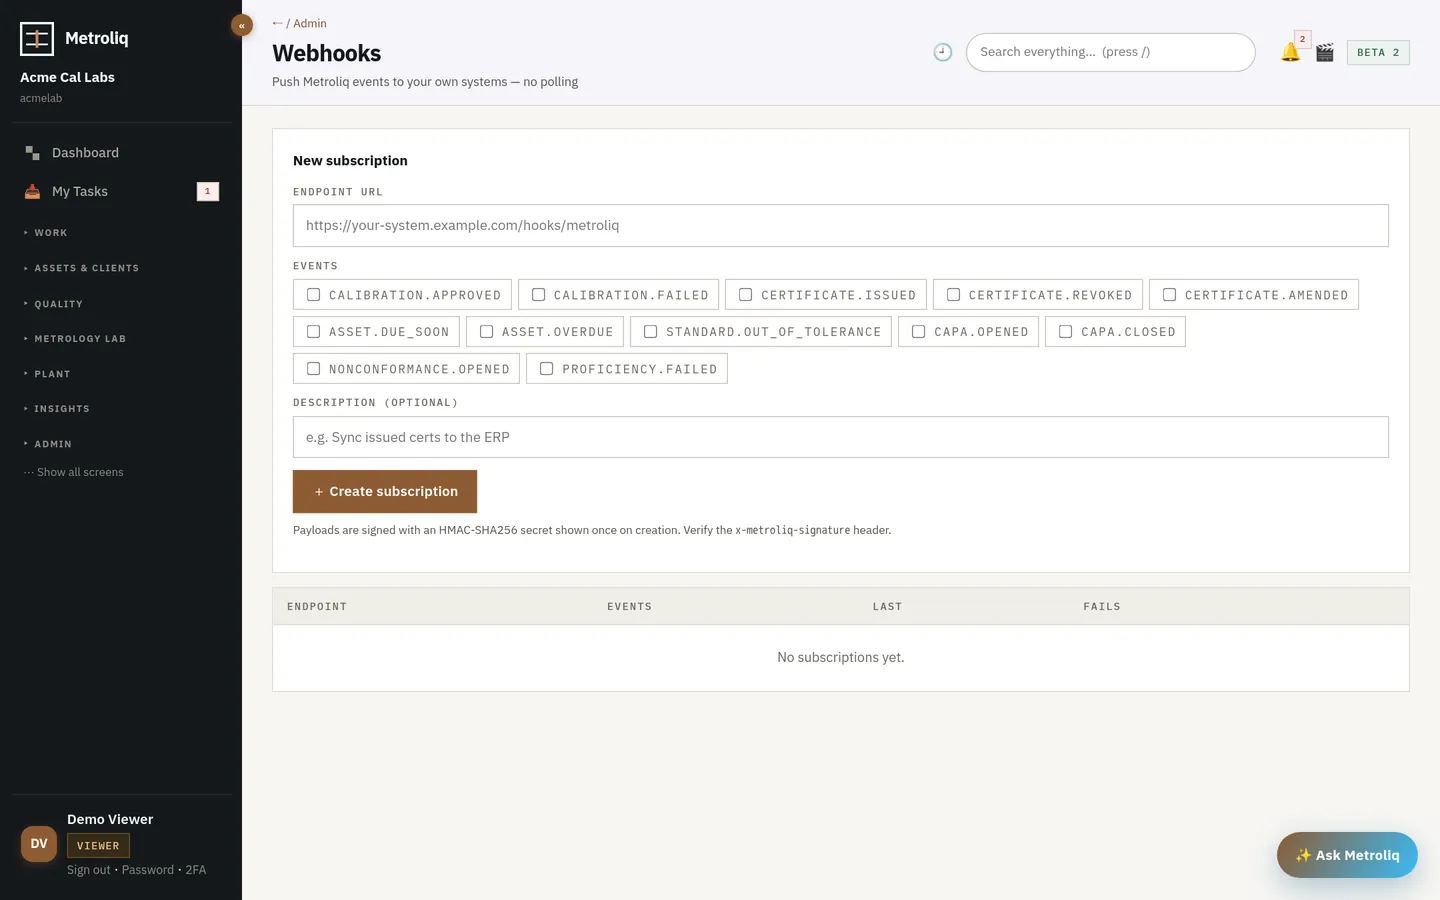
The web app is a client of the same REST API you get: versioned, bearer or API-key authenticated, idempotent on writes, with signed webhooks on every state change and a DCC for every certificate.
This page is the orientation, not the full reference. The full route list is in the product under Settings → API, and the demo tenant answers real requests.
https://platform.metroliq.com/api/core. Send x-api-version: 1; the response echoes it. Unsupported versions are refused with 400, never silently downgraded.
Authorization: Bearer <session token> for people; X-Api-Key: crt_… for systems. Keys carry a read or write scope and are hashed at rest. OAuth2 client-credentials tokens (RS256 JWT, one-hour expiry, scoped, verifiable via JWKS) are available for machine-to-machine access.
Send Idempotency-Key on POST, PUT and PATCH. A retry replays the stored response with idempotency-replayed: true; a reuse on a different route is refused with 422.
JSON {error} with the HTTP status that means it: 400 unknown field or bad value, 401/403 auth, 404 wrong tenant or missing, 409 state (already approved, slot taken, stale standard), 422 idempotency misuse, 423 locked, 402 module not in plan.
Every record is scoped to your workspace. A record you cannot see is a 404, and the isolation suite proves it on every build.
The full OpenAPI 3.1 spec is generated live from the running router at /openapi.json, with Redoc documentation at /docs, a ready-to-import Postman collection, and generated JavaScript/Python client stubs.
| Group | Examples | What they do |
|---|---|---|
| Assets & standards | /assets /assets/:id/history /standards /tools/capable | Register, hierarchy, custody, history, reference standards with per-point accuracy, capability search |
| Calibration | /events /events/:id/perform /events/:id/approve /events/:id/standards /events/:id/points | Lifecycle draft → performed → approved; points, readings, standards, environment |
| Uncertainty | /uncertainty/studies /uncertainty/montecarlo /uncertainty/sensitivity /uncertainty/risk /msa/grr | GUM budgets, Monte Carlo, sensitivity coefficients, PFA/PFR, Gage R&R |
| Certificates | /events/:id/certificate /certificates/:id?format=html|pdf|dcc /certificates/:id/amend /dcc/import /public/cert-verify | Issue, render in three formats, amend, revoke, import DCC, public verification |
| Quality | /ops/:entity /ops/ncr/:id/escalate /ops/capa/:id/effectiveness /qms/analytics /qms/audit-readiness | Eighteen record types with status machines and e-sign gates |
| Maintenance & assets | /ops/work_order /pm/generate /cbm/rules /assets/:id/meters /failure-codes | Work orders, PM, condition rules, meters, failure vocabulary |
| Manufacturing | /mes/start-batch /ops/batch_record/:id/step /ops/lot-trace /ops/oee | Batches, steps, exceptions, genealogy, OEE |
| Service & portal | /service-requests /service-requests/:id/transition /customers /portal/* | Orders, documents, clients, the customer portal |
| Inventory | /inventory/items /inventory/items/:id/issue /purchase-orders/from-low-stock | Lots, FEFO issue, alerts, purchasing |
| Platform | /webhooks /api-keys /workflows /import/analyze /audit/verify /validation/oq/run /lifecycle/export | Webhooks, keys, workflow engine, imports, audit verification, validation kit, export |
Every state change emits a signed POST. Verify x-metroliq-signature (HMAC-SHA-256 over the body with your hook secret), de-duplicate on x-metroliq-delivery, and reply 2xx. Three attempts with backoff.
| Event | When |
|---|---|
| calibration.performed | A technician signs the performed event |
| calibration.approved | The approver signs |
| certificate.issued | A certificate number is assigned and rendered |
| certificate.amended | A new revision supersedes the old |
| asset.due_soon / asset.overdue | Calibration due within the window, or past it |
| standard.out_of_tolerance | A reference standard failed its own calibration or check |
| capa.opened / capa.closed | A CAPA is raised or closed after its effectiveness check |
| nonconformance.opened | An NCR is raised |
| proficiency.failed | A PT/ILC result is unsatisfactory |
POST /events with an asset, a decision rule, the standards and the points. Then POST /events/:id/perform with the readings and the technician's password as signature; the response carries the verdict per point, TUR, guard band and PFA.
POST /events/:id/approve with the approver's password (a different user when independent approval is on). Then POST /events/:id/certificate returns the number; GET /certificates/:id?format=dcc returns the DCC XML for the customer's system.
Ask for a demo API key in the contact form and try it against the demo tenant.
The tour runs the working platform, not a mockup. Pilot on your own instruments with your own imported history — we set it up with you, and fixes ship in hours and days, not release cycles.