In the product
The controls, on screen
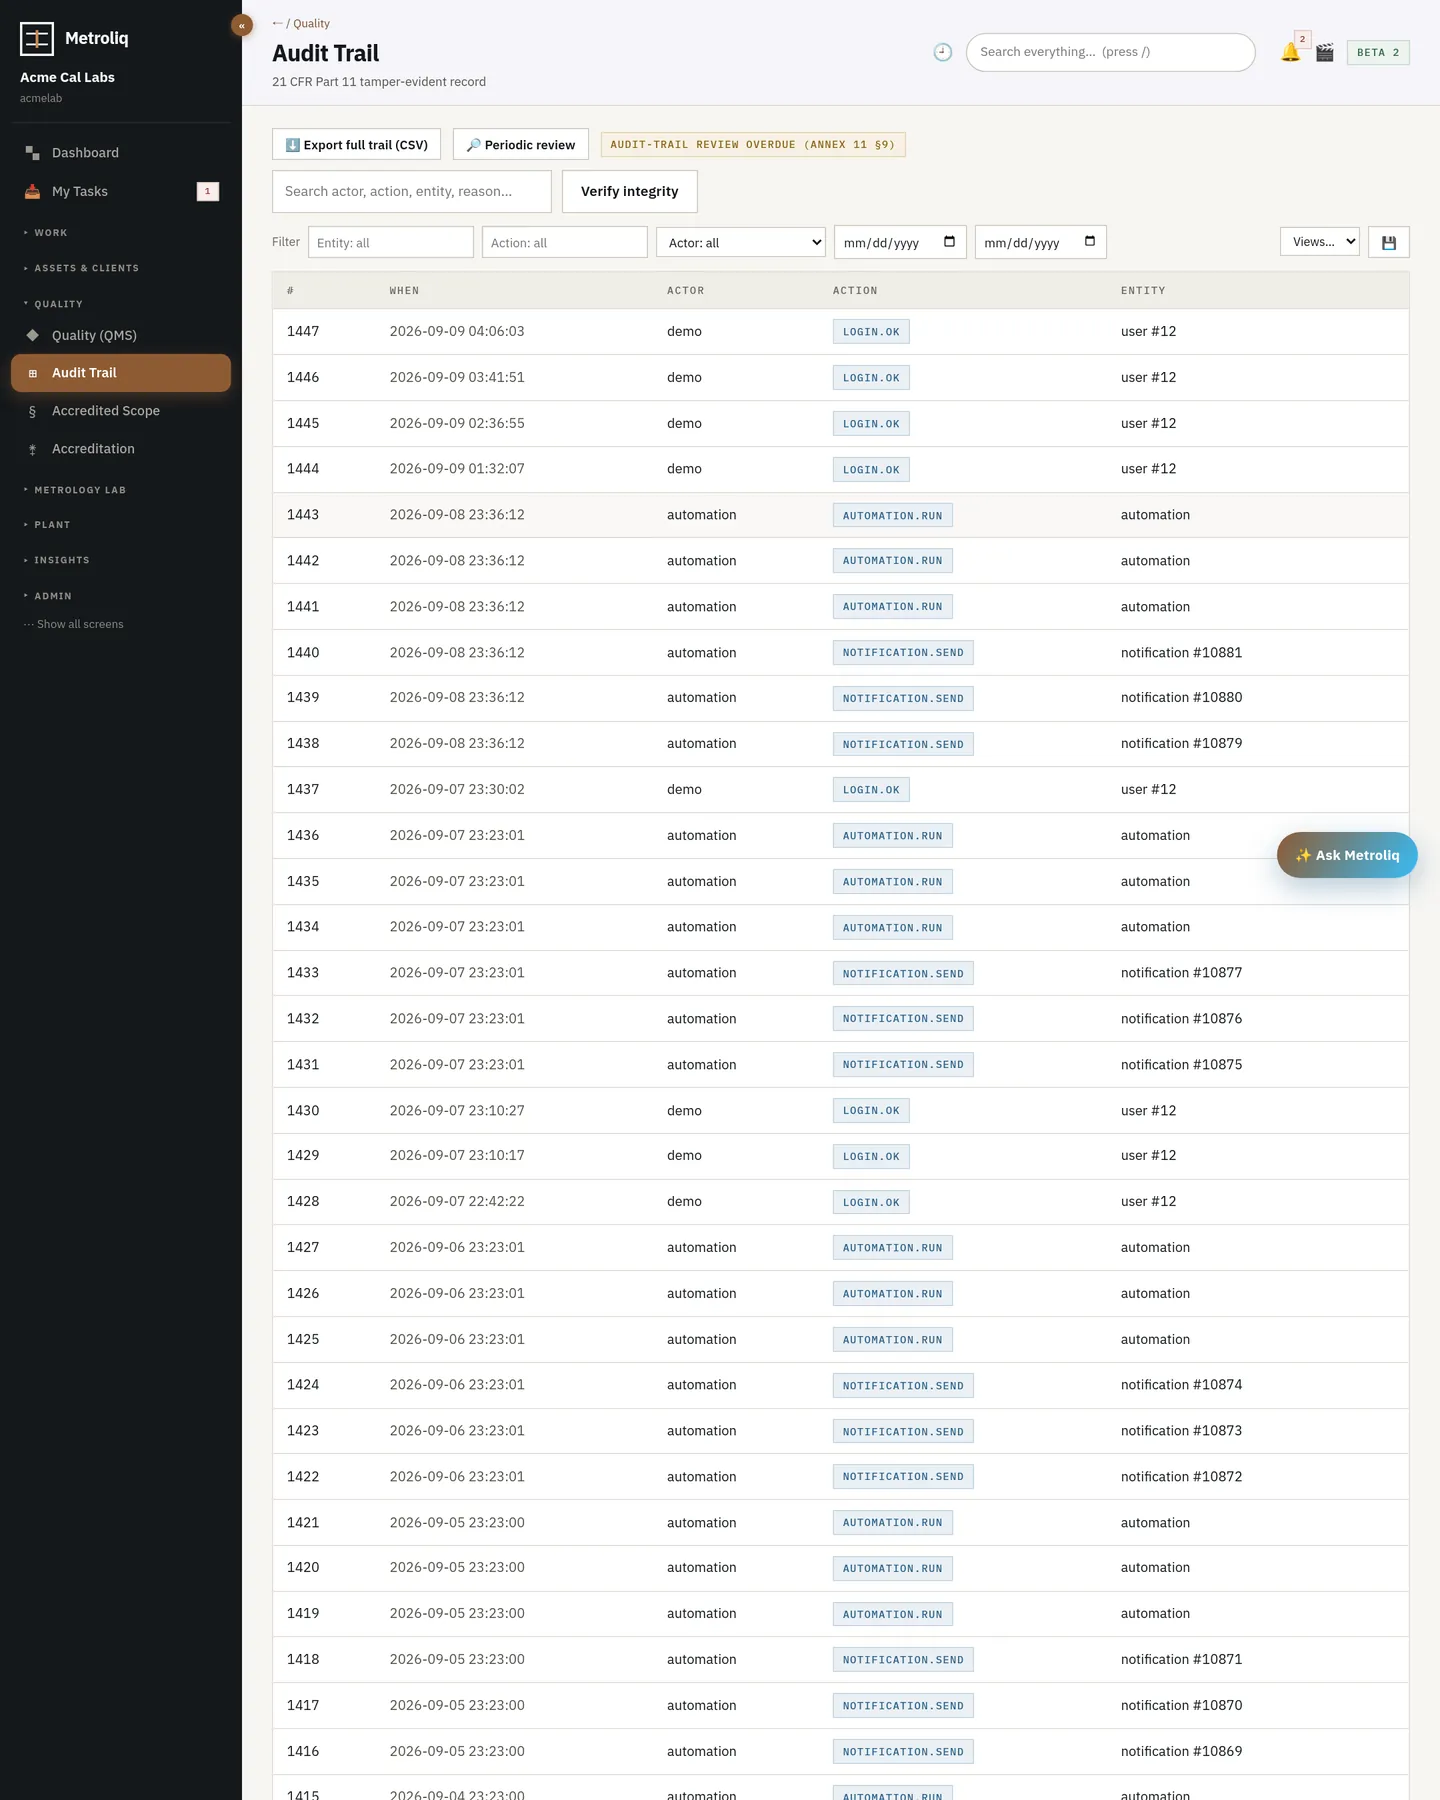
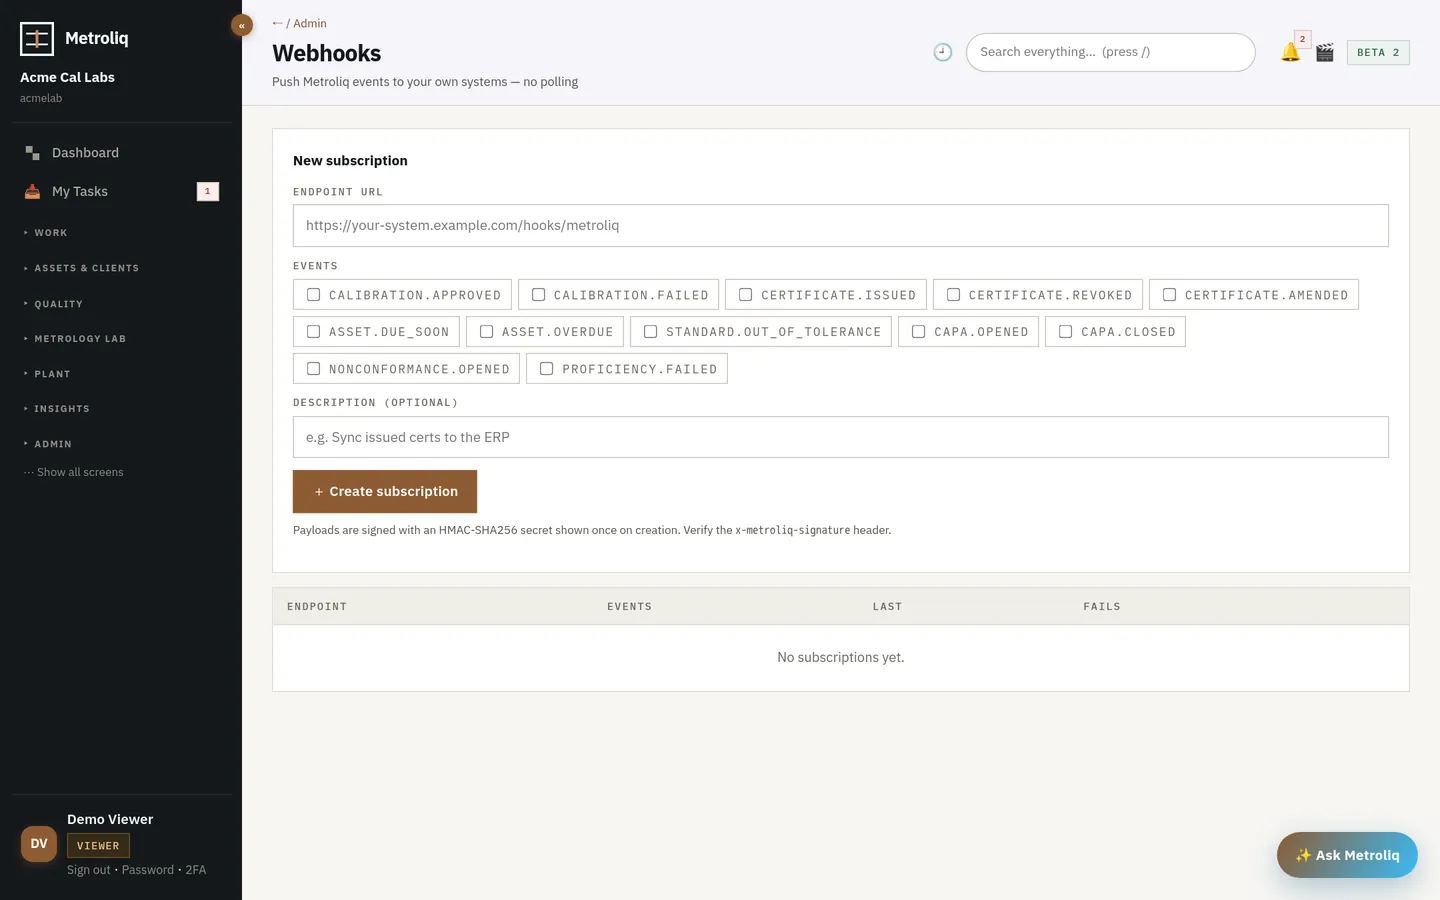
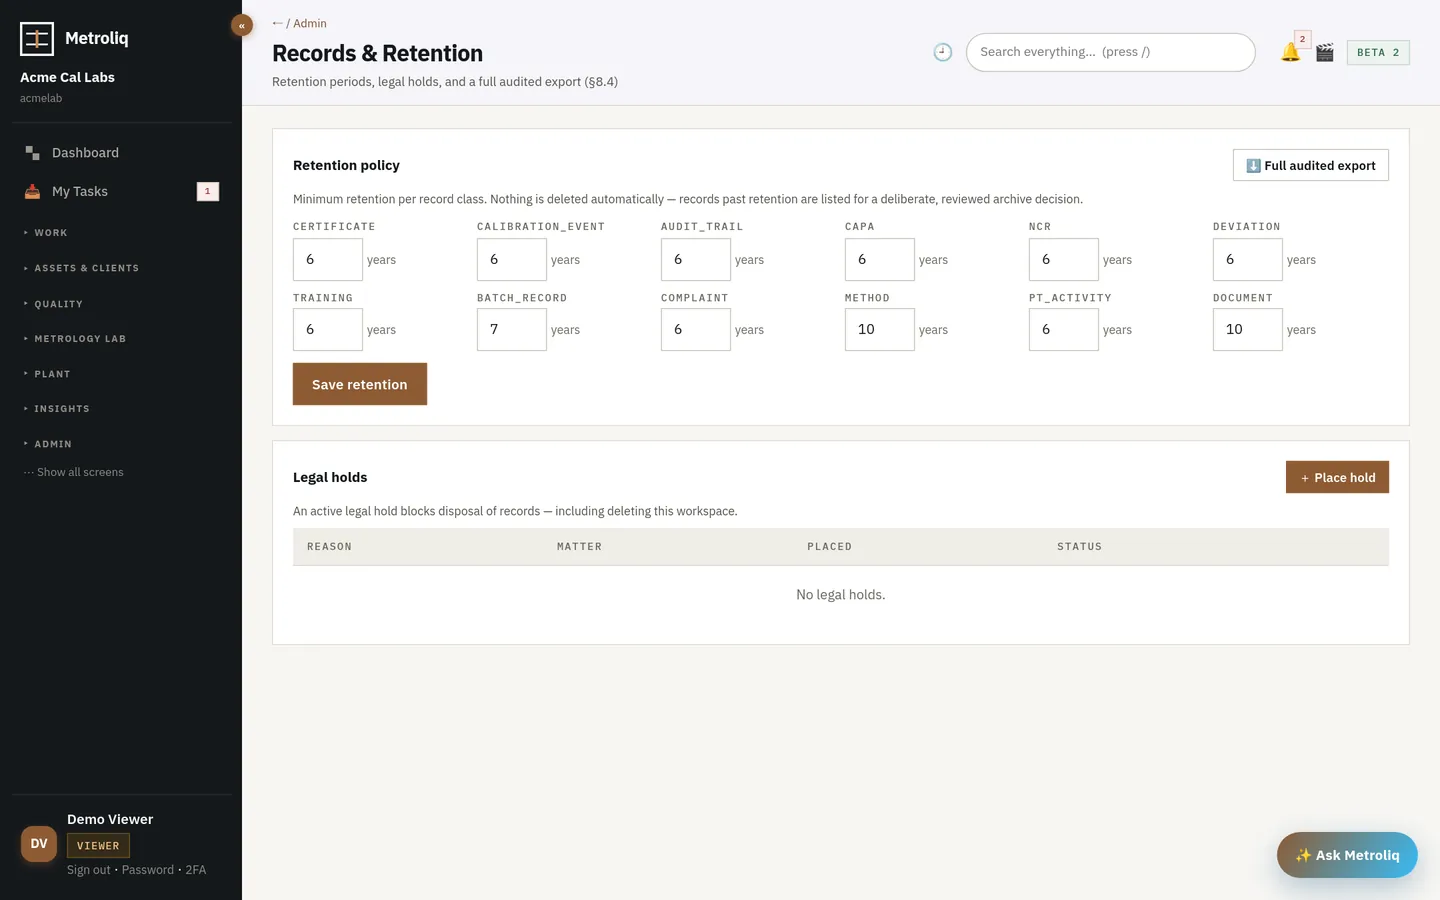
No SOC 2 or ISO 27001 certificate yet, and we will not pretend otherwise. What we have is a set of controls you can inspect: scrypt-hashed passwords, opaque sessions, TOTP two-factor, SSO with signature verification, SCIM provisioning, row-level tenant isolation with its own test suite, a hash-chained audit trail, signed webhooks, and nightly backups with a weekly restore test.
Everything on this page is taken from the code or the running system. Where a control does not exist, it says so.
How a request travels and what each layer enforces.
Controls are listed here and can be inspected in a pilot, now backed by a SOC 2 / ISO 27001 Annex A controls matrix mapping each control to evidence, and by automated ZAP and npm audit scan results. Certifications will be announced when they exist.
Data at rest is protected by host and disk controls, not by application-level encryption. Database connections can require TLS.
Length, expiry, lockout and 2FA are enforced; reuse prevention and complexity classes are on the list.
A content-security policy ships on the web app, tuned for certificate and report iframes, PDF downloads and the customer portal. Directives were tightened — frame-ancestors, worker-src, and no wildcard image sources — and it is not yet in report-only/strict-nonce mode. Inline scripts remain and are documented.
The platform runs as containers behind a Cloudflare tunnel. On-premise deployment for contracted customers uses the same containers.
Tell us from inside the product (the built-in helper escalates to a human with the context attached) or through the pilot request form on the demo. We fix in hours and days and will credit you if you want it.
Do not test against other tenants' data. Use your own workspace, or ask for a throwaway one: onboarding creates a tenant in seconds.
The tour runs the working platform, not a mockup. Pilot on your own instruments with your own imported history — we set it up with you, and fixes ship in hours and days, not release cycles.